Mythic C2 Activity at Internet Scale
17.9.2026 CENSYS CyberCrime
Mythic is an open-source collaborative C2 framework which is actively maintained on GitHub. It provides a plugin-based architecture supporting multiple agent types, transport profiles, and an operator-facing web UI.
Mythic has a suite of features that help facilitate post-compromise control across many phases of the attack chain. Red team practitioners use it for authorized engagements while it has also been observed in unauthorized intrusions by threat actors.
As of September 11, 2026, Censys tracks 131 unique hosts exposing Mythic on the public Internet; 115 of those carry a certificate with O=Mythic or O=Mythic C2 as the subject organization, which is the default configuration.
Mythic was created as a successor to an earlier macOS-focused project (Apfell). It was designed as a language-agnostic, cross-platform framework with a web-based UI. It is provided in a dockerfile to suit your environment with the ability to choose and configure separately available agents. This modular design lets operators combine agents for different platforms with various transport profiles without modifying the core framework. These agents, C2 profiles, wrappers, and services are shared and supported by the Mythic Community.
The framework’s documentation is thorough and publicly available. It is used in authorized penetration tests and red team assessments. Its extensibility, multi-operator support, and public documentation also make it accessible to threat actors.
Remote command execution via an interactive task queue and shell access across platforms.
Multi-agent, multi-operator support with a browser-based UI, role-based access, and shared campaign context.
Modular transport profiles (HTTP/HTTPS, WebSocket, TCP, SMB named pipes, DNS) switchable without redeploying agents.
File staging and transfer with upload/download task tracking.
Credential access and post-exploitation through agent-side modules for keylogging, screenshot capture, token impersonation, and LSASS interaction (Windows agents).
Lateral movement support through SMB pipe-based agent pivoting and SOCKS proxy chaining.
Payload generation with configurable obfuscation, sleep jitter, and kill-date parameters.
Mythic’s default deployment emits several fingerprints detectable in Censys scan data:
|
Artifact |
Detail |
|---|---|
|
TLS certificate subject |
O=Mythic or O=Mythic C2, self-signed, ECDSA-SHA384. 98 hosts carry O=Mythic; 21 carry O=Mythic C2; 115 carry at least one. |
|
Internal PKI chain |
CN=operators (issuing CA) → CN=multiplayer (server cert). Default installer values; appear unchanged on 6 tracked hosts. |
|
Port 7443 response |
Mythic’s Nginx reverse proxy returns HTTP 502 for unauthenticated requests, producing a consistent, identifiable response. |
Ten of the 131 tracked hosts carry an additional C2 framework alongside Mythic:
6 also expose Sliver, 6 expose Adaptix C2, 1 exposes Havoc, and 1 exposes FRP
(Fast Reverse Proxy). Some hosts combine multiple. While maliciousness and
intent cannot be divined from co-location or the lack of it, insights and
couched assessments can be made from examining these patterns along with
additional context.
Three hosts (68[.]178[.]202[.]150, 68[.]178[.]205[.]17, 192[.]169[.]176[.]54) share an identical port fingerprint: 22, 53, 80, 500, 4321, 7443, 8001, 8081, 31337. All three carry the same self-signed certificate: C=UK, ST=England, L=Birmingham, O=demo, OU=cyber. Mythic, Sliver, and Adaptix C2 appear across all three; Havoc is present on 192[.]169[.]176[.]54. Reverse DNS is GoDaddy’s generic auto-assignment (*.host.secureserver.net); no custom domain is configured on any host.
Four C2 frameworks on a single IP, an O=demo certificate, no custom domain, and an identical nine-port fingerprint across three adjacent hosts on the same provider point to a shared lab or training fleet, not an operational deployment. Operational infrastructure typically isolates tools across hosts and keeps its port footprint narrow. This profile is the opposite.
Four hosts (65[.]87[.]7[.]11, 194[.]26[.]192[.]117, 142[.]93[.]52[.]11, 170[.]64[.]183[.]242) run Mythic and nothing else. They share the same JARM on port 7443 (1dd40d40d00040d00042d43d000000831b6af40378e2dd35eeac4e9311926e), the same nginx/1.25.5 banner, and the same login page body hash. Two hosts (65[.]87[.]7[.]11 and 194[.]26[.]192[.]117) share an SSH host key. The cluster carries a custom domain, telemetry-update[.]services, on port 443 with a spoofed Server: NetDNA-cache/2.2 header and Content-Type: application/javascript; charset=utf-8 on 404 responses. That combination mimics a CDN edge node; agent traffic goes to port 443 and operator traffic goes to port 7443.
The staging server at 65[.]87[.]7[.]11:4444 is publicly accessible and shows active tool development. Eleven sequential Windows PE builds of a payload family named “nyx” (nyx-v5.exe through nyx-v15.exe) sit alongside Rust source for a second family, “fys2” (fys2_config.rs, fys2_src.tar.gz). A /serve/ subdirectory holds current build outputs staged for victim download. Seven Discord diagnostic scripts (discord_check.py, discord_diag.py, discord_probe.py, and four more) indicate Discord is a production C2 transport, not an experiment. Steganography scripts (stego_roundtrip.py, discord_fix2/stego.py) and a ChaCha encryption test (chacha_stage_test.py) sit alongside Mythic tasking scripts (mythic_task.py, mythic_whoami.py, mythic_shell.py).
The single-framework footprint should not be interpreted as evidence of limited capability. The operator is building custom Rust implants across eleven build iterations, running a Discord-based transport layer with steganographic staging, and using Mythic as the operator-side framework, all behind a domain name built to blend with Windows telemetry traffic.
Query:
host.services.threats.name: "Mythic" or web.threats.name: "Mythic"
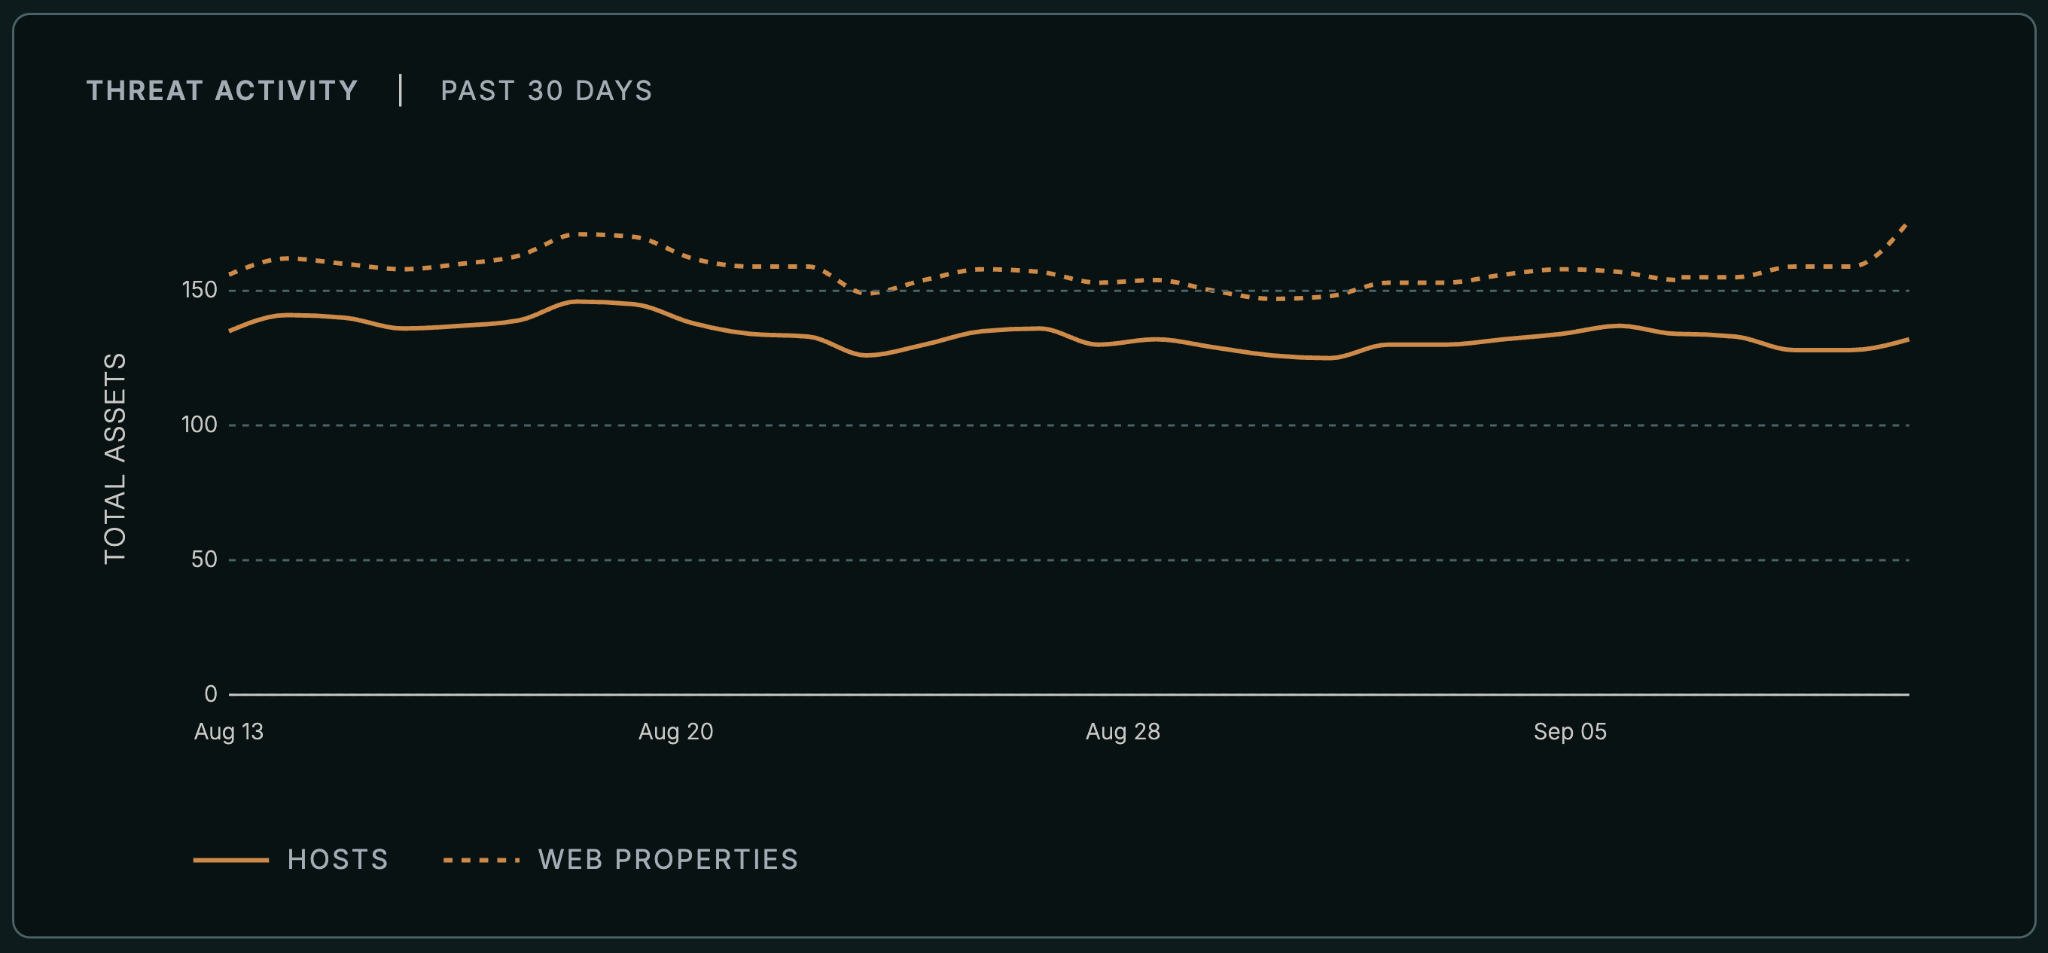
Censys tracks 131 unique hosts matching this query as of September 11, 2026, across 307 total service hits.
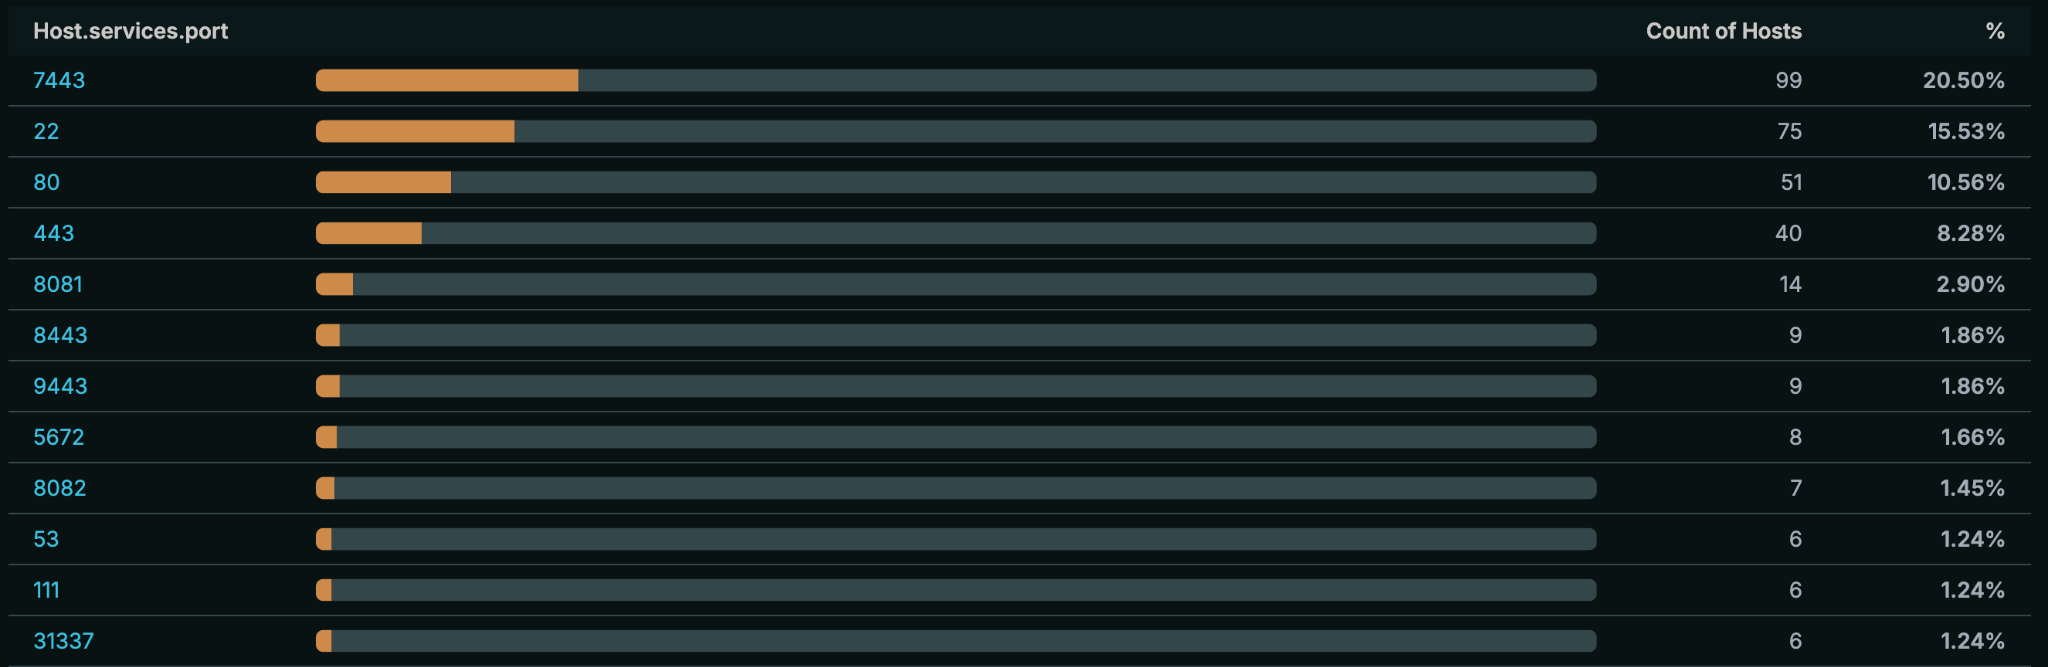
Port 7443 appears on 99 hosts (20.5%). Many operators deploy without changing the default web UI port. Ports 80 (51 hosts) and 443 (40 hosts) also appear across this population; the aggregation counts all open ports on matched hosts, so those numbers reflect the broader service footprint, not necessarily a distinct count of Mythic profile listeners. Port 8081 appears on 14 hosts, 9443 on 9 hosts, and 31337 on 6 hosts.
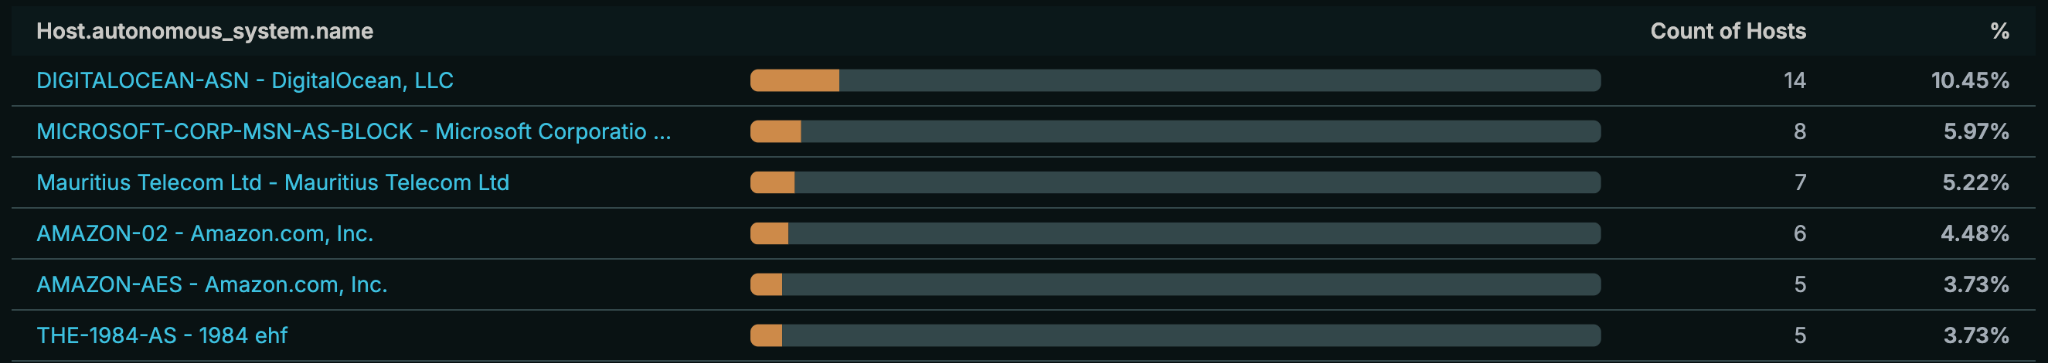
ASN distribution: DigitalOcean leads with 14 hosts (10.45%), followed by combined AWS services (11 hosts, 8%) and Microsoft Azure (8 hosts, 6%). Mauritius Telecom (ASN 23889) accounts for 7 hosts across two adjacent cities: Beau Bassin-Rose Hill (3 hosts) and Quatre Bornes (4 hosts). Iceland’s 1984 ehf (AS 1984) hosts 5 servers.
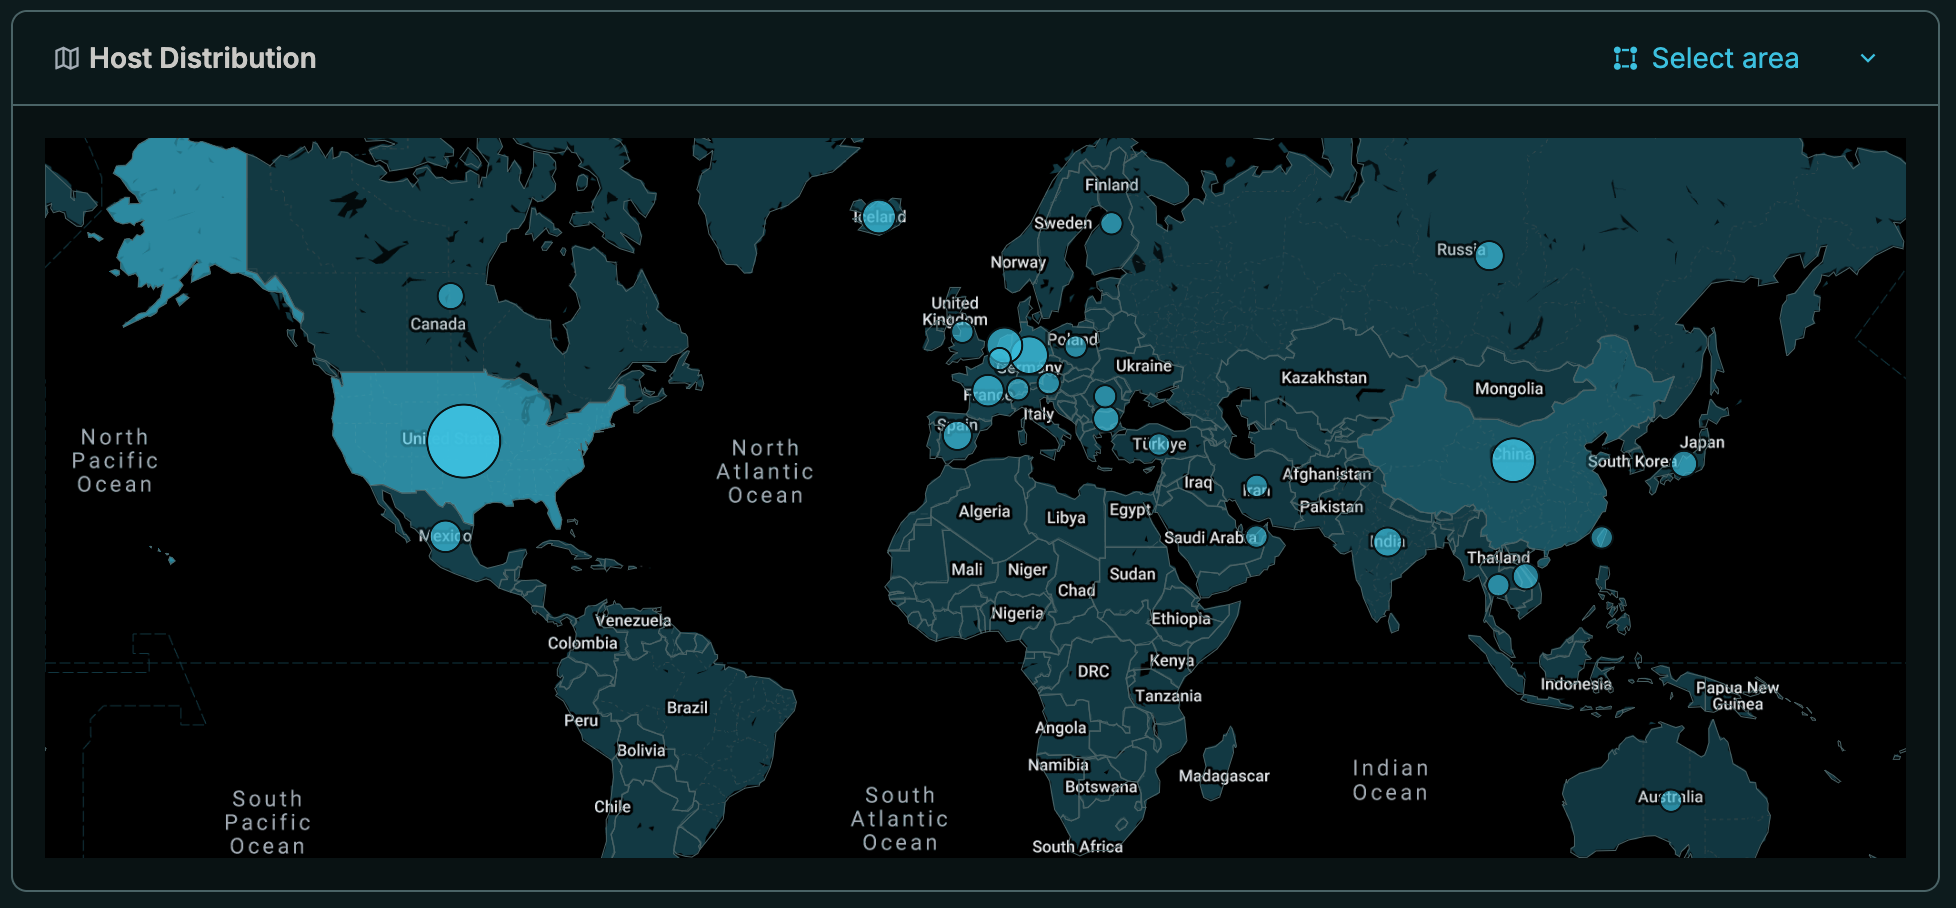
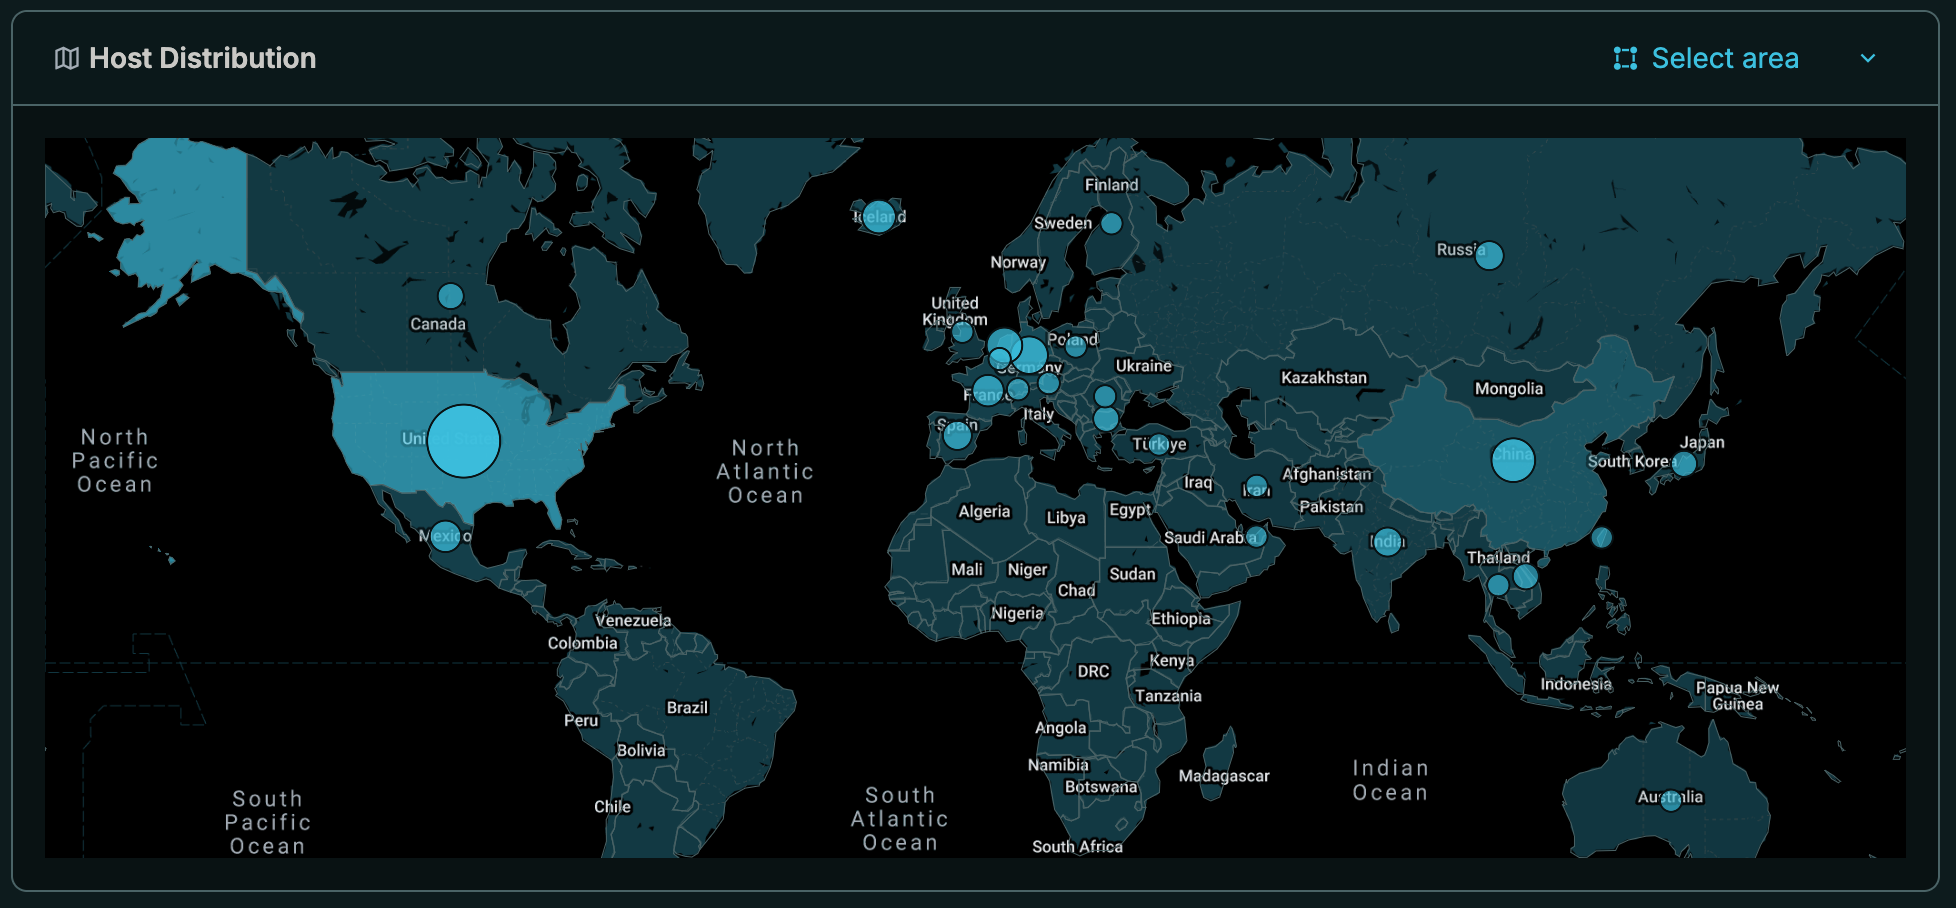
Geolocation: The United States accounts for 42 hosts (32%), followed by Hong Kong (11 hosts, 8%), China (10 hosts, 8%), Germany (7 hosts, 5%), Mauritius (7 hosts, 5%), the Netherlands and Singapore (6 each).
Of hosts where the OS was identified, 98.5% run Linux. At the time of the query only a sole Windows host was observed as the outlier.
The certificate fingerprints O=Mythic and O=Mythic C2 subject DNs together cover 115 hosts (88%). The CN=operators → CN=multiplayer certificate chain appears on 6 hosts; these run Mythic’s default internal mTLS without modification.
Because of Mythic’s ability to deploy a variety of both known and unknown agents (which complicates host based detection), proactively identifying Mythic C2 hosts is a strong first layer of defense. Mythic’s default deployment leaves multiple fingerprints that defenders can use in detection rules immediately.
Alert on TLS connections to servers presenting O=Mythic or O=Mythic C2 as the certificate subject organization.
Flag outbound connections to port 7443 on dedicated VPS or cloud IPs with no known legitimate service, especially when the TLS cert is self-signed.
Monitor for CN=operators and CN=multiplayer on servers your organization communicates with. These are Mythic’s internal PKI defaults.
Alert on Docker Compose deployments including mythic_nginx, mythic_rabbitmq, or mythic_server container names in your infrastructure (which may indicate unauthorized tooling deployment from a threat actor or an unsanctioned engagement).
Flag unexpected scheduled tasks, launch agents, or systemd units pointing to binaries in temp or user directories. These are common persistence mechanisms for Mythic agents.
On Windows targets, watch for process injection and LSASS access from non-system processes. Apollo, Mythic’s primary Windows agent, uses standard injection techniques.
Run the query above in the Adversary Investigation module in the Censys Platform to download the current Mythic host list. In the Censys Platform (non Adversary Investigation module), query host.services.cert.parsed.subject_dn: "O=Mythic", which will return hosts carrying the default Mythic certificate. Cross-reference against your egress network telemetry to identify internal hosts communicating with suspected Mythic infrastructure.