| DATE |
|
NAME |
INFO |
CATEGORIE |
WEB |
|
28.8.26 |
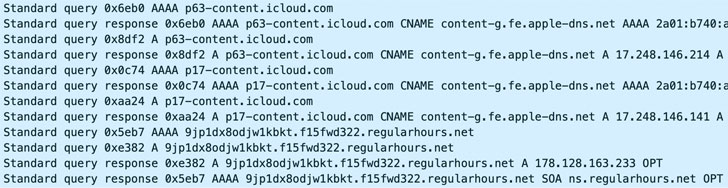 |
ValleyRAT masquerading as adware |
Attackers typically try to
pass off malware as legitimate applications or as potentially unwanted programs
that users deliberately search for and download, such as cheats or cracks. They
often rely on ad and affiliate networks to deliver their creations to victims’
devices. This post examines a less conventional case: a well-known backdoor
distributed under the guise of adware. The attackers may have chosen this
distribution method because the adware was signed by the developer. On top of
that, users often manually add these apps to exclusions, so their useful
features don’t get blocked. |
Virus |
SECURELIST |
|
28.8.26 |
 |
Some Malicious PE Stats |
During my last FOR610 session, a student asked me if I had some statistics in
mind about the compilers used to generate malicious PE files? A couple of months
ago, I shared some stats about the trend in 64bits VS. 32bits malware[1]. Can we
go a bit further? I (vibe-)coded a Python script based on the pefile library[2]
to extract some info from the PE headers. Indeed, the PE file format contains a
lot of metadata! They can be accessed using a lot of tools, like Detect It Easy: |
Virus |
SANS |
|
28.8.26 |
 |
A polymorphic phishing page (that occasionally breaks itself) |
As I’ve mentioned before in some of my diaries, from time to time,
I like to go over phishing messages that get caught in my various spam traps or
sent to us here at the Internet Storm Center. |
Phishing |
SANS |
|
28.8.26 |
 |
Who Has Admin Rights in your Entra ID Directory? |
A common thing that folks
should "worry" about in Entra (or any platform really) is "who has
rights to administer"? Who can delete or change key things, or modify
them in ways that might not be obvious (accidentally or on purpose). Yes,
we trust our people, but if they've moved on to other roles or to other
organizations, they change from "our people" to "used to be our people". |
Security |
SANS |
|
28.8.26 |
 |
Threat
landscape for industrial automation systems. Q2 2026 |
In Q2 2026, the percentage of ICS computers on which malicious objects were
blocked continued to decrease, reaching its lowest level since 2022 — 19.15%. |
ICS |
SECURELIST |
|
26.8.26 |
 |
Exploits and vulnerabilities in Q2 2026 |
The vulnerability
landscape shifted significantly in Q2 2026. First, the number of registered CVEs
reached an unprecedented level. This is driven primarily by the widespread
adoption of AI, both for application development and search for security flaws.
This resulted in entire new classes of vulnerabilities emerging, particularly in
the Linux networking subsystem. |
Exploit |
SECURELIST |
|
26.8.26 |
 |
Obfuscating IP Addresses as Hostnames |
It is pretty obvious
that hostnames can replace IP addresses. Pretty much any software accepting an
IP address will also accept a hostname as an argument. Last week, I wrote about
scans for the cloud metadata service listening at 169.254.169.254. These scans
attempted to exploit Server Side Request Forgery (SSRF) vulnerability. One way
to prevent these types of exploits is to filter requests that contain the string
"169.254.169.254" or to add this IP to a blocklist of URLs that should not be
accessed. |
Hack |
SANS |
|
24.8.26 |
|
DOUBLECUP's PNG
Payload |
New malware that uses steganography always gets
my attention, but I was disappointed when I looked at the latest DOUBLECUP
write-up. It doesn't use real
steganography: |
Virus |
SANS |
|
23.8.26 |
 |
(FRIDAY):
SMARTAPESG CLICKFIX CAMPAIGN LEADS TO TWO RATS |
Zip files are password-protected. Of note, this site has a new password
scheme. For the password, see the "about" page of this website. |
MALWARE TRAFFICS |
malware-traffic-analysis |
|
21.8.26 |
|
The invisible passenger in your car |
While monitoring Android threats in June 2026, we discovered a
new piece of Android malware. What struck us as unusual was that it installed
like an ordinary user app yet made no attempt to disguise itself as legitimate
software: it had no user interface at all. This led us to suspect the app might
be reaching users’ devices without their knowledge. Further investigation
confirmed that hypothesis and allowed us to reconstruct the entire infection
chain. |
Virus |
SECURELIST |
|
21.8.26 |
|
Even MOAR Powershell, looking at Entra logins - the good, the bad and the
password sprays |
One thing that folks never seem to do after "going to the
CLOOOOUUUUD" is to look at their logs, logs that they would have checked daily
when things were on premise. |
Security |
SANS |
|
21.8.26 |
|
Who Got Missed in the MFA Rollout? More Powershell + Graph + Entra scripting! |
In
every MFA rollout, there will come a time where you think you are closing in on
"done", and some automation to list what's left would be handy. Something
quicker than scrolling through the web interface through thousands of accounts
... |
Security |
SANS |
|
20.8.26 |
 |
Using Microsoft Graph and Powershell - Risk Detection Commands |
Building on the last diary on Using MS Graph and Powershell,
let's look at "Risky" logins. |
OS |
SANS |
|
20.8.26 |
|
Using Microsoft Graph and Powershell to Mine for Information - Stale Accounts
and Licenses |
Microsoft Graph is a newer API that is meant to replace several others. OK, it's
at version 2.3.9, so it's not all that new, but it's new enough that lots of
folks (and commercial tools) aren't using it yet. It allows you to Get and Set
info from/to M365, Entra Users and Entra managed machines for starters. Let's
dig in! |
OS |
SANS |
|
19.8.26 |
 |
Simple Scans for Cloud Metadata Service |
Cloud providers typically expose a REST API at 169.254.169.254 that allows code
running on virtual machines to retrieve machine-specific data. Some of the data
is more or less harmless, such as the region the machine is running in or its
MAC and IP addresses. However, the service may also be used to retrieve
credentials for IAM roles and service account tokens. |
IT |
SANS |
|
18.8.26 |
 |
Apple Patches iOS and macOS |
Apple today released updates for
iOS/iPadOS (26 and 18) and macOS 26. This update fixes 108 vulnerabilities and
comes about two weeks after the much smaller macOS update that addressed the
single screen-sharing vulnerability. This vulnerability did not affect iOS/iPadOS.
|
OS |
SANS |
|
18.8.26 |
|
Apple Screen Sharing Security |
About 20 years ago, with macOS 10.5 (Leopard), Apple introduced
screen sharing. Apple did not invent a new protocol for screen sharing. Instead,
it used the established VNC protocol. VNC is a pretty simple, unencrypted protocol
using TCP port 5900. Historically, the protocol used a simple global password
for authentication. Apple adapted the protocol for its own use, but overall,
left the VNC protocol itself alone. |
OS |
SANS |
| 17.8.26 |
 |
UNISOC T612 LPE |
UNISOC (Shanghai) Technologies Co., Ltd. is a top-three global fabless
semiconductor company headquartered in Shanghai, specializing in 2G/3G/4G/5G
mobile communication, IoT, and smart device chipsets. Formerly Spreadtrum, it
serves major brands like Honor, realme, vivo, Samsung, and Motorola, with
products in over 140 countries. |
Vulnerebility |
SSD-DISCLOSURE |
|
13.8.26 |
 |
Armored Likho expands its cyber-espionage toolkit |
In May 2026, we discovered a new cyber-espionage campaign by the
Armored Likho group, also known as Eagle Werewolf, that targets private
individuals and organizations across various industries in Russia, including
major corporations, the public sector, IT, and education. The attackers used a
fake app as bait that mimics a service for donations. However, the most
interesting part of this campaign isn’t the initial infection method – it’s the
malicious implants the attackers use for cyber-espionage. |
APT |
SECURELIST |
|
13.8.26 |
|
(WEDNESDAY): SMARTAPESG CLICKFIX LEADS TO TWO RATS |
Zip files are password-protected. Of note, this site has a new password scheme.
For the password, see the "about" page of this website. |
MALWARE TRAFFICS |
malware-traffic-analysis |
|
13.8.26 |
 |
Using Gemma4 with Ollama - Testing File Hash Analysis and
Recommendations with AI
|
In
the past few weeks, I have been using Gemma4 as a Large Language Model (LLM) to
see how useful it can be to analyze some of the malware hashes uploaded to the
DShield sensor over the past 30 days and figure out how its recommendation can
be considered useful about the activity my DShield sensor is collecting and
tracking. The model I use for this testing is gemma4:e4b [2] using two sites to
compare the data against VirusTotal and CyberGordon. |
AI |
SANS |
|
13.8.26 |
 |
Linux Kernel Process Accounting |
A
couple of days ago, Xavier posted about Atuin to gain more insight into the
command history. Atuin does a great job of better organizing what is usually
handled by "bash_history" and collecting meaningful additional data. Our reader
David commented that this can also be done quite well with Linux's kernel
process accounting feature, and I think he is very right. I really like Linux
process accounting for a number of reasons, so here is a quick introduction.
|
OS |
SANS |
|
12.8.26 |
|
Microsoft Patch Tuesday August 2026 |
This month we got patches for 418 vulnerabilities. Of these, 62
are critical, 1 is being exploited in the wild, and 2 were publicly disclosed as
zero-days. Notable fixes include Windows privilege escalation, container
tampering, and critical QUIC and DNS Server remote code execution bugs.
|
OS |
SANS |
|
11.8.26 |
|
LUMMA STEALER OR VARIANT
|
Zip files are password-protected. Of note, this site has a new password
scheme. For the password, see the "about" page of this website. |
MALWARE TRAFFICS |
malware-traffic-analysis |
|
10.8.26 |
 |
IT threat evolution in Q2 2026. Mobile statistics |
The mobile section of the quarterly cyberthreat report includes statistics on
malware, adware, and potentially unwanted software for Android, as well as
descriptions of the most notable threats for Android and iOS discovered during
the reporting period. These statistics are based on detection alerts from
Kaspersky products, collected from users who consented to provide statistical
data to Kaspersky Security Network. |
Mobil |
SECURELIST |
|
10.8.26 |
|
IT threat evolution in Q2 2026. Non-mobile statistics |
Microsoft has dismantled an
illicit malware-signing service used by ransomware operators. Microsoft’s
Digital Crimes Unit has shut down a malware-signing-as-a-service (MSaaS)
operation run by the threat group Fox Tempest. The illicit service abused the
Microsoft Artifact Signing platform to generate digital signature certificates
for malicious software. Malware signed by these certificates was observed in
campaigns conducted by such ransomware groups as Rhysida, Akira, INC, Qilin, and
BlackByte. |
Mobil |
SECURELIST |
|
10.8.26 |
 |
Targeted espionage activity UAC-0226 against innovation centers,
government and law enforcement agencies using the GIFTEDCROOK stealer (CERT-UA#14303)
|
The
Ukrainian government's computer emergency response team, CERT-UA, has been
monitoring targeted activity for the purpose of espionage against centers of
innovation development in the military sector, military formations, Ukrainian
law enforcement agencies, and local governments, especially those located along
the country's eastern border, since February 2025. |
BigBrothers |
CERT UA |
|
8.8.26 |
|
Linux Shell Forensic: Let?s Dive Into Atuin! |
UNIX systems (including Linux) are well-known to record a lot of activities in
many different locations. But there is one domain where they definitely lack of
"modern" logging: shells. Most shells provide an historization of the typed
commands through a flat file in the $HOME directory (ex: $HOME/.bash_history).
They suffer of multiple problems: |
OS |
SANS |
|
6.8.26 |
|
22 Seconds to Compromise: How Automated SSH Actors Move From
Login to Persistence Before You Can Blink |
On
May 23, 2026, a threat actor successfully authenticated to my Cowrie SSH
honeypot using compromised credentials and, within 22 seconds, injected a
backdoor SSH key, changed the root password, attempted to clear host-based
access restrictions, and performed automated system reconnaissance. The speed
and consistency of the behavior left no room for doubt: this was not a human
attacker manually working through a system. |
Hack |
SANS |
|
6.8.26 |
|
Don't Revoke That Token Yet: Inside the keyv/cacheable npm Worm
|
When you learn that a compromised package executed on one of your build hosts,
muscle memory takes over: revoke the npm token, rotate the GitHub PAT, cycle the
cloud keys. That reflex has been correct in almost every supply-chain incident I
have worked. In the keyv/cacheable compromise that has been unfolding since
yesterday, it is the one thing you should not do first — because revoking the
stolen token is exactly what arms the payload. |
Hack |
SANS |
|
4.8.26 |
|
Botnet Hunting for Vulnerabilities in Diagnostic Tools
|
This morning, I noticed specific sources "hunting" for vulnerabilities in URLs
that I haven't noticed before. All of these URLs appear to be associated with
diagnostic tools: |
Vulnerebility |
SANS |
|
3.8.26 |
|
Analysis of a Phishing Email Attack Case by the Larva-24009
Threat Actor
|
The Larva-24009 threat actor has been active since at least 2023, carrying out
phishing email attacks targeting users both in Korea and globally to install
malware. ASEC (AhnLab SEcurity intelligence Center (ASEC) has previously
disclosed attack cases by this threat actor in 2024, and Subsequently,
Cyble also identified this same attack campaign and named it “HeptaX.” The
Larva-24009 threat actor continues to carry out attacks in 2026, and this report
summarizes the attacks and malware identified in 2026. |
Phishing |
AHNLAB |
|
2.8.26 |
|
Atomic MacOS (AMOS) stealer infection |
This diary provides indicators from an Atomic MacOS (AMOS) stealer infection
that I generated in my lab on July 31st, 2026. This was distributed through a
web page from getmacouscloud[.]com with instructions to paste text into a macOS
Terminal window, supposedly for "macOS toolkit," but instead the text is a
command to retrieve and install AMOS stealer malware.
|
Virus |
SANS |
|
1.8.26 |
|
Phishing Campaigns Targeting AI Solutions Providers |
Most phishing campaigns rely on the fact that the victim is afraid to loose "something":
money, access to information, ... Many brands have been impersonated by
campaigns but I spotted some phishing emails that focus on AI services like
ChatGPT.
Yesterday, I found this email that was properly designed but also sent with a
very good timing: the end of the month when your classic billing process is
restarted! |
Phishing |
SANS |
|
|
|
|
|
|